Most Credit Union Cybersecurity Incidents Start With a Vendor

Your Year-End Board Briefing Should Start There, Too.
I've spent many years around banks and credit unions, and the year-end board briefing on cybersecurity usually goes the same way. Somebody puts up a slide about ransomware; somebody else asks if we've got it covered; the answer is yes, and everybody moves on to the loan portfolio.
In the first year of the 72-hour cyber incident reporting rule, credit unions filed 1,072 incident reports with the NCUA. 742 of them involved a third party. That's roughly seven out of ten incidents with a vendor somewhere in the story. The NCUA shared those figures in its October 2024 board briefing.
So if your board meeting gets one cybersecurity conversation, I'd make it about the vendor list.
Your vendor list grew one reasonable decision at a time.
Nobody sets out to have 24 vendors touching member data. It happens the way almost everything in cybersecurity happens at credit unions: the core, then digital banking, then card processing, then the loan origination system, the statement printer, the e-signature tool, the marketing platform, and the consultant who needed access for one project in 2023 and still has it.
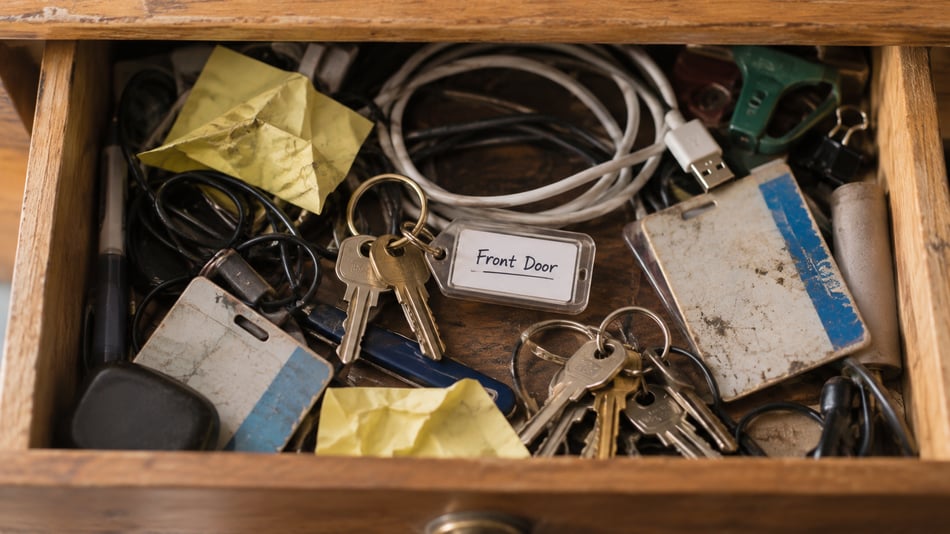
Every vendor list looks a little like the junk drawer in the kitchen. Everything in there was put there for a good reason, and nobody's quite sure whether half of it is still needed or any good.
That's where incidents come from. Complex systems fail at human seams, and a vendor connection is a seam with somebody else's staff, somebody else's patching schedule, and somebody else's owner on the other side. We've written before about what happens when a vendor's ownership changes, and the support quietly changes with it.
To be fair to the vendors, most of them are doing solid work, and a credit union can't run without them. The issue is that nobody on your side is assigned to watch the connection after go-live.
The key in the junk drawer that nobody knows what it unlocks anymore is dangerous in a bank's cybersecurity plan!
Five questions your board should ask:
A managing board doesn't need to understand the technology. They need to ask questions that have names and dates for answers.
1. Which vendors can reach member data, and who on our staff owns each relationship? A list with an owner next to every line. If a line has no owner, that's the first thing to fix.
2. When did we last review what each vendor can access? Access controls need to be monitored constantly as people, vendors, and technology changes.
3. If a vendor calls tomorrow and says they've had an incident, who picks up the phone, and who starts the 72-hour clock? The rule gives you 72 hours from the time you reasonably believe a reportable incident occurred. That's a short window to spend figuring out whose job it is to make the decisions that keep you compliant.
4. Which vendor contracts say when they have to tell us? Some say 24 hours. Some say "promptly." Some don't say anything at all.
5. When did somebody last restore from backup and write down how long it took the vendors to get us back online? A vendor outage and a restore test are important conversations, especially in the age of AI cyber threats.
Start with these action items:
- Build the vendor inventory this month, with an owner for each vendor.
- Pull the access review for the five vendors closest to the core.
- Write the one-page call tree for a vendor incident and walk through it once at a staff meeting.
Next quarter is fine for the contract review, the tabletop exercise, and the conversation with your insurance advisor about how your IT team, your carrier, and your leadership review risk together.
A full vendor management platform can wait. A spreadsheet with owners beats a platform nobody opens or one that takes months to get right.
Where your IT team fits with your MSP
Most credit unions I talk to have a small, sharp internal IT team that already knows where the gaps are. They don't need replacing. They need support. They need time, and vendor reviews are exactly the kind of work that gets lost in the ticket queue every week.
Co-managed IT gives that team reinforcement on scheduled, documented work, and they keep the architecture, decisions, and relationships. We laid out how that works in Credit Union IT in 2026.
If you're not sure where your credit union stands on any of those five questions, request a leadership or board briefing with Solve iT. You'll get a plain-English read on your vendor seams, what to fix first, and what can wait.
We'll also be at the Carolinas Credit Union League's LAUNCH conference in February, so if you're going, come find me.
Quick Answers
What causes most credit union cyber incidents? According to NCUA figures from the first year of its 72-hour reporting rule, 742 of 1,072 reported incidents involved a third party such as a vendor or service provider.
What is the NCUA 72-hour rule? Federally insured credit unions must notify the NCUA within 72 hours of reasonably believing a reportable cyber incident has occurred. The rule took effect September 1, 2023.
What should a credit union board ask about vendor risk? Ask which vendors can reach member data, who owns each relationship, when access was last reviewed, what each contract says about incident notice, and who starts the 72-hour clock.
Does co-managed IT replace a credit union's internal IT team? No. Internal IT keeps architecture, decisions, and vendor relationships. The co-managed partner takes scheduled work such as patching, backup verification, and access reviews.