You Can't Automate a Process That Doesn't Exist

Most business leaders we talk to want the exciting part of AI and technology. They want the dashboard that predicts the bottleneck, the assistant that drafts the email, the report that writes itself.
Very few want to talk about user offboarding, data classification, or the spreadsheet that exists in three versions on three laptops.
That gap is where AI projects go to stall.
In Episode 7 of Shh... IT Happens, "From Vision to Value: How Technology Maturity Powers Executive Strategy," co-host John Ohlwiler, CEO of Sentry Technology Solutions, walked through the technology maturity model he built for business owners.
Since October is Cybersecurity Awareness Month, we're using this episode to start a four-part series on AI and security. It begins with the level most businesses want to skip.
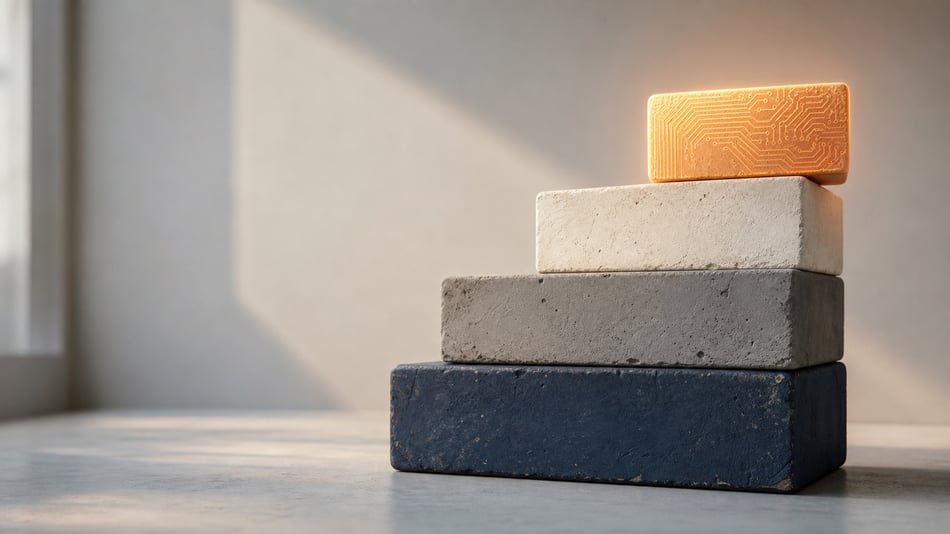
Technology maturity has four levels, and each one holds up the next
John's model breaks technology into four stages:
- Operational IT. Help desk support, onboarding and offboarding users, what happens when the internet goes down. The cost of doing business.
- Cybersecurity and compliance. Protecting data and meeting the rules that apply to your industry and your state.
- Business integrations. Systems that talk to each other, and departments that talk to each other with IT in the room.
- Business innovation. Automation, AI, and the large returns everyone wants.
"There are some ways to try and jump ahead," John said, "but it usually doesn't work out great." Eddie's shorthand for that approach: ready, fire, aim.
John also made a point that should comfort smaller companies. "Size doesn't necessarily dictate level of maturity." A 20-person firm with clean processes can be further along than a 2,000-person company without them.
Level two is the floor your AI plans stand on
Security spending is easy to resent. John compared it to car insurance: if the car has never been in a crash, the policy feels like pure expense.
That feeling is why leaders are tempted to rush past level two. It's also why the rush backfires.
The security and compliance layer has grown so large it now maps to formal frameworks. The practical questions are simple, though: how you classify your data, where you store it, and who can reach it.
Those answers decide what any AI tool can safely touch later.
In plain English, an AI assistant inherits the permissions of the person using it. If everyone in the company can open every folder, their AI can too.
At Solve iT, we describe security as people, process, and technology, in that order. That helps us put the correct cybersecurity in place.
The Workday rollout shows what skipping IT costs
John shared a story from a company with more than 2,000 employees. HR brought in Workday, a powerful platform, without really involving IT or finance.
Instead of connecting it to single sign-on, meaning one login tied to the company's existing Microsoft 365 identity, they issued separate usernames and passwords to everyone. A month or two later, the private equity firm that owns the company renewed its cyber insurance. It had told the carrier the business used multifactor authentication. Then it asked how Workday handled that. Nobody had an answer.
They had to rip out the logins and rebuild them. Finance ended up reconciling benefit accruals by hand after every pay period. The company still can't use features it paid for.
"That cleanup process is frequently more painful than spending the time to get it right out of the gate," Eddie said.
The fix is a Solve iT position we repeat often: bring IT in before the contract is signed. We made the same case in If IT Isn't at Your Strategy Table.
You can't automate a process that doesn't exist
"It's very hard to automate a process that doesn't really exist," John said. His favorite example is a room of ten people who all do the same job ten different ways. Management likes how Sally does it and how Jim does it, but nobody has combined the two into a standard.
Standard operating procedures help, only if people follow them, someone measures them, and someone updates them. Otherwise you get the Friday report that still goes out because the procedure says so, long after a live dashboard replaced it.
His best success story predates the AI boom. Before food delivery apps existed, Domino's connected its stores and tracked every pizza from order to oven to door. The app even sends a two-minute warning, which John noted gives you time to get the dog into the backyard.
The innovation worked because the basics worked. "If you go to that app and it only worked four out of five times, chances are people wouldn't use it," John said. Domino's had to get operations, security, and integration right before the fun part paid off.
John tied the same logic to the current wave of AI disappointment.
MIT's 2025 GenAI Divide research found that 95% of organizations reported no measurable profit-and-loss impact from their formal generative AI investments. John's read: "A lot of it boils down to garbage in, garbage out."
We'd add that garbage in, garbage out now comes with a turbocharger.
Shadow AI is already inside most businesses
In the Tool Time segment, I cited the same MIT research. Only 40% of companies had purchased official AI subscriptions, yet employees at more than 90% of companies regularly used personal AI tools for work.
That is shadow AI: AI use the company hasn't approved and often can't see. John explained that a managed IT provider can usually see how much time people spend on a tool like ChatGPT. It can't see what they typed into it.
The episode also opened with a Harvard Business Review article from September 2026, "Is Your AI Training the Competition?" The author argues that enterprise AI contracts usually protect prompts and outputs, while the feedback and direction your people give the tool can still teach the platform how your business thinks.
Veronica's takeaway was right: before you use an AI tool, ask what happens if a competitor ends up benefiting from what you put in. Otherwise, Shh.. IT might happen.
We'll go further into personal AI accounts and who owns the work inside them next week.
For background, our July post, Shadow AI Is Entering Your Business From All Sides, covers how it gets in.
The practical fix
Start with these, in order:
- Rate yourself honestly on each level. Most businesses sit at different levels in different departments. That's normal.
- Close level-two gaps before funding level-four projects. Multifactor authentication and single sign-on on every business app, regular access reviews, and a clear map of where sensitive data lives.
- Put IT in the room before you buy. HR platforms, CRMs, accounting tools, and AI tools all touch security and data.
- Write down how the work actually gets done. Pick the best version of each process before you try to automate it.
- Ask your team which AI tools they use. Then move business work into company-owned accounts.
What can wait: privately hosted AI models, custom agents, and large automation projects. They'll deliver more once the foundation is in place.
Where Solve iT fits in
Solve iT lives in levels one and two every day: support, monitoring, security, backup, and documentation. We also push to be in the room for level three, because that's where most expensive mistakes get made.
We find much better success for our clients when they involve us in those crucial conversations.
A maturity rating isn't a report card to dread. We're giving you a gap analysis and a potential roadmap so that you can plan things out and reduce downtime, reduce risk.
If you want the full conversation, including John's Domino's breakdown and the shadow AI segment, listen to Episode 7 of Shh... IT Happens. You'll get a plain-English framework for deciding which technology projects are ready now and which ones need groundwork first.
Listen on Buzzsprout, Apple Podcasts, Amazon Music, or YouTube.
Quick Answers
What is a technology maturity model? A way to rate how ready a business is for more advanced technology. John Ohlwiler's model uses four levels: operational IT, cybersecurity and compliance, business integrations, and business innovation.
Why do AI projects fail in small businesses? Most stall because the basics beneath them are unfinished: undocumented processes, scattered data, and loose access controls. AI speeds up whatever process it touches, including broken ones.
Should cybersecurity come before AI adoption? Yes. Access controls, multifactor authentication, and data classification determine what an AI tool can reach, so they should be in place first.
What is shadow AI? Employees using AI tools the company hasn't approved or can't see, often through personal accounts.